Overview
See the engine in action.

Watch on YouTube
EU AI Compliance Engine — From Crisis to Authority™
Who it's for
Built for organisations
that cannot afford to fail audit.
Designed for high-risk AI providers, deployers, and their advisors — across every sector subject to EU AI Act obligations.
Economic impact
The compliance cost
of doing it the old way.
EU AI Act compliance for a single high-risk system typically requires months of consulting engagement. The EACE Engine changes that equation.
01 — Core Engine
EU AI Compliance Engine (EACE)
A complete, version-controlled compliance operating system for the EU AI Act. Covers every risk tier, every deployment context, and every relevant EU regulation — generating a cross-referenced evidence package structured for notified bodies and market surveillance authorities.
Document architecture — sample preview
Architecture
Five engines — a Decision Engine, two Compliance Packages (Provider, Deployer) and two Governance tracks (Transparency, Baseline) — routed by risk classification result. Each engine contains structured Ultra Modules generating deterministic, reproducible outputs. All outputs are cross-referenced, version-controlled, and carry a structured evidence layer (EID/MEI) with full audit trail.
Coverage
150+ documents across ten document families (Fast Start, Foundation + Families A–H, plus the GDPR & ePrivacy External Template Suite). Sector overlays for employment, healthcare/MedTech, and finance/banking/AML. Country overlays for all 27 EU member states and 3 EEA countries.
Five engines
Decision Engine
Territorial scope & risk classification
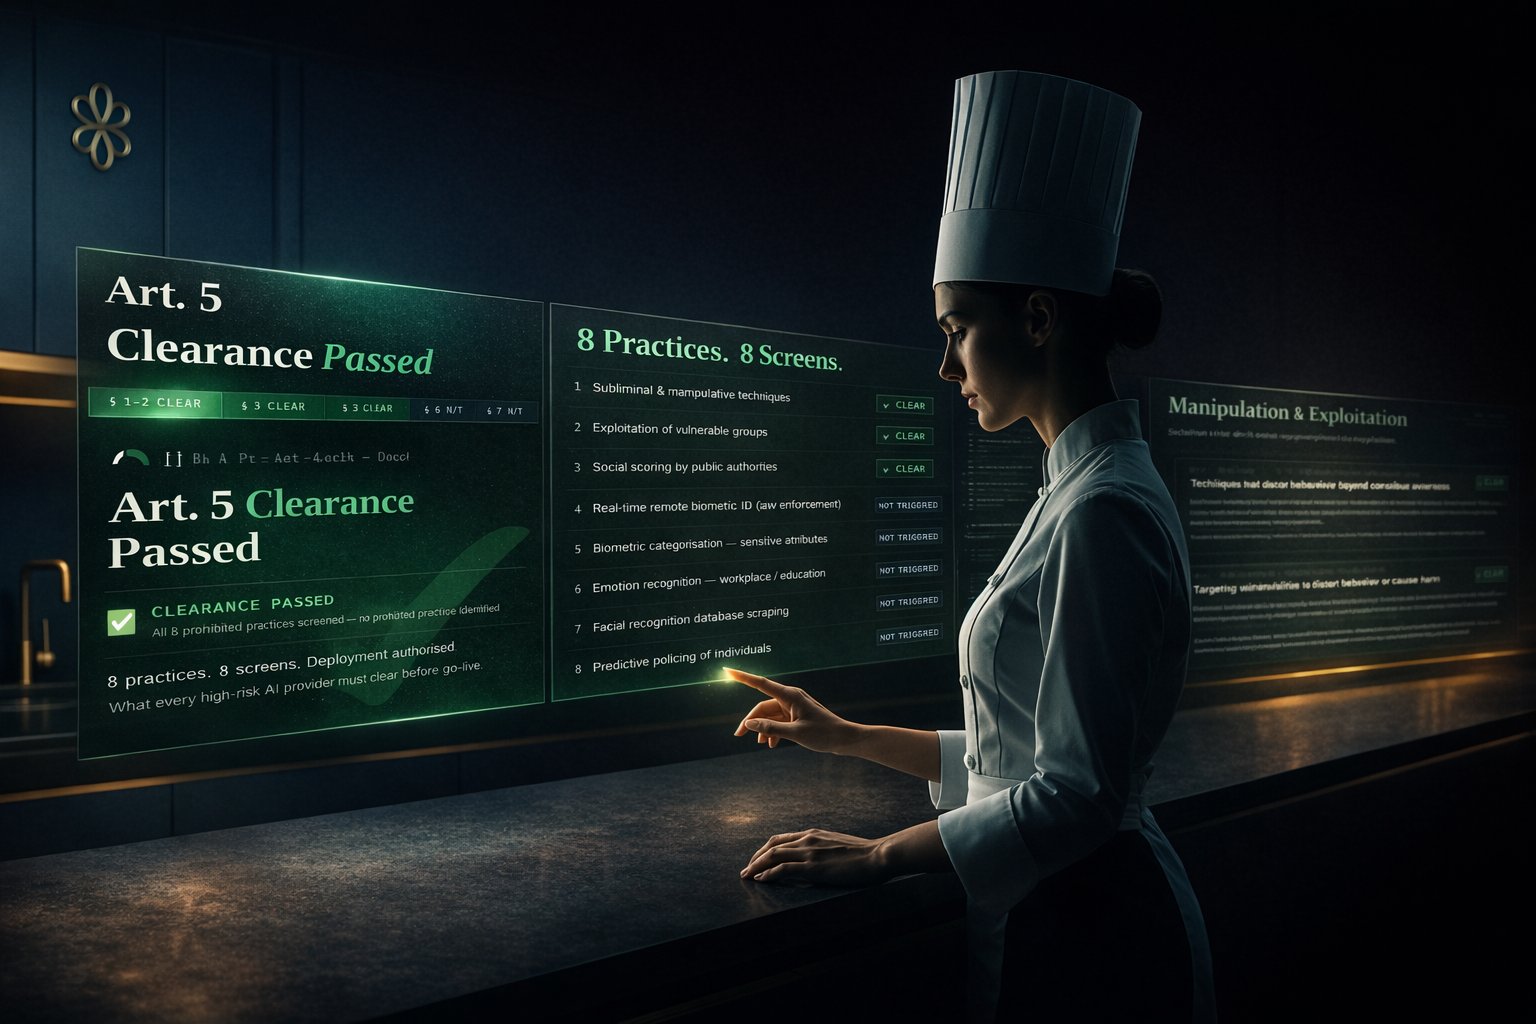
Jurisdiction · applicability · risk tier routing · Art. 5 clearance
Compliance Package — Provider
High-risk provider compliance
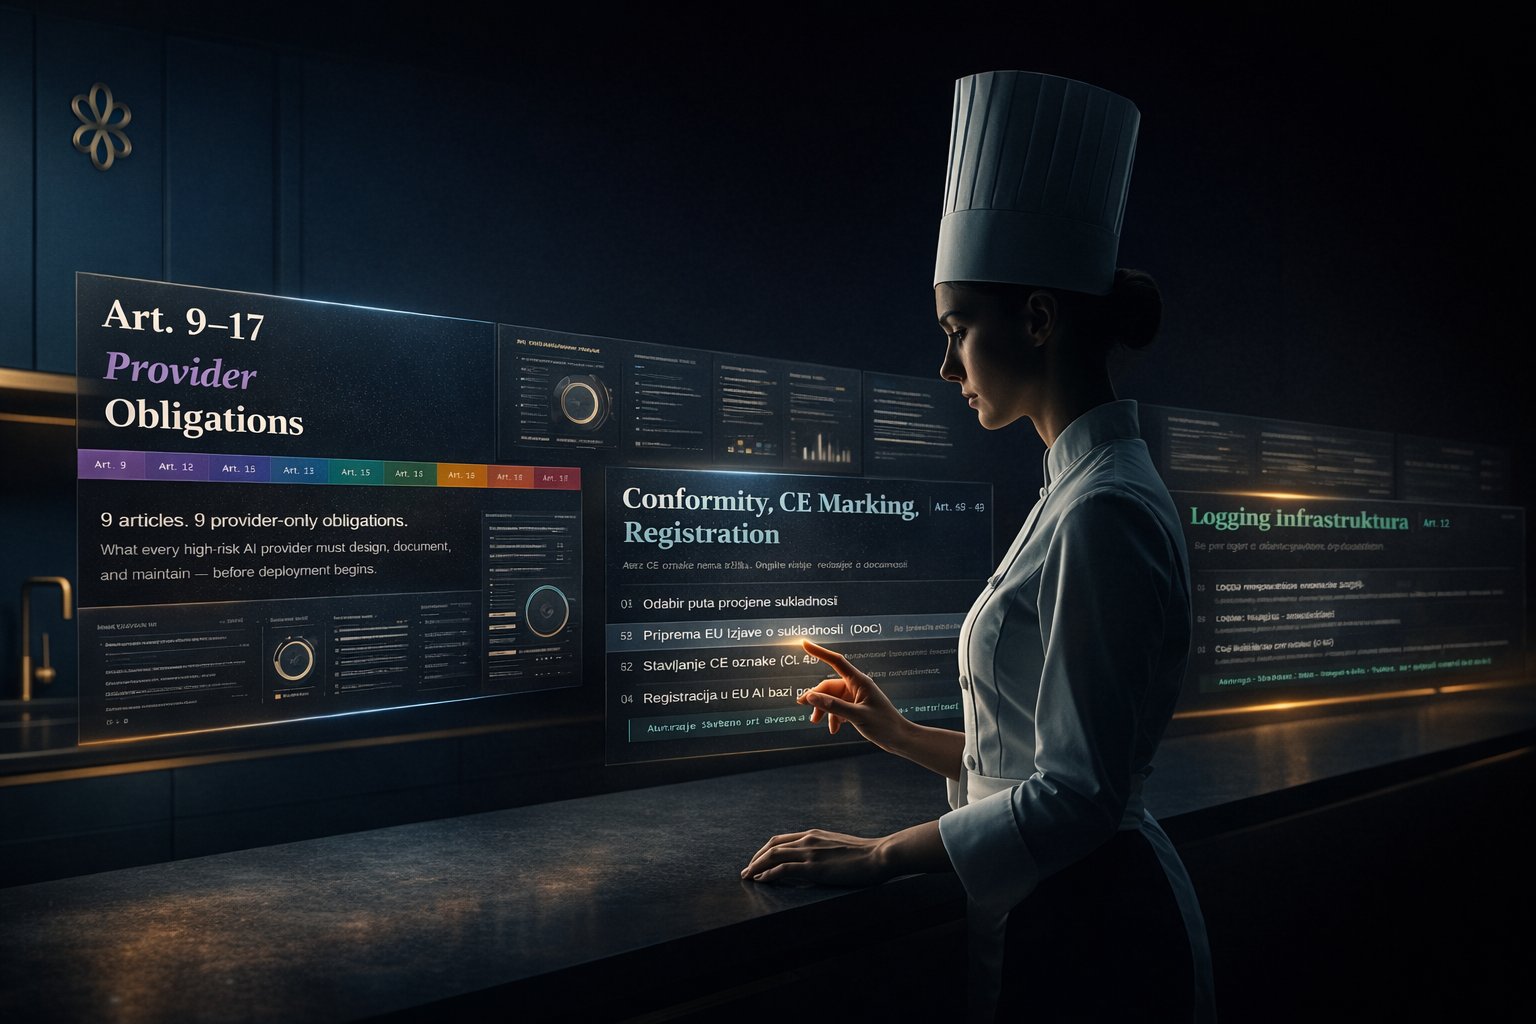
Arts. 9–17, 43, 47–49, 51–55, 72–73
Compliance Package — Deployer
High-risk deployer compliance
Arts. 26–27, 50 · Full operational lifecycle
Governance — Transparency
Limited-risk transparency
Art. 50 · Art. 26(11)
Governance — Baseline
Minimal-risk documentation
Art. 6(3) · Art. 95
Structured output categories — per engine
Decision Engine — Classification
Scoping & routing outputs
Compliance Package — Provider
Provider compliance outputs
Compliance Package — Deployer
Deployer compliance outputs
Governance — Transparency
Limited-risk transparency outputs
Governance — Baseline
Minimal-risk documentation outputs
Document families — 150+ documents across 10 families
FAST START
Quick start guide & workflow overview
FOUNDATION
Core components, navigation guide, glossary, transition guide, licensing & commercial documents
7 documents
FAMILY A
Classification, territorial scope & evidence layer (Decision Engine)
Decision Engine · Evidence layer · CSV specs
FAMILY B
High-risk compliance — provider & deployer (Compliance Package)
Architecture · Provider & Deployer editions · Evidence · CSV
FAMILY C
Transparency & limited risk (Governance — Transparency)
Art. 50 · Art. 6(3) · Evidence layer
FAMILY D
Minimal risk documentation (Governance — Baseline)
Art. 95 · Evidence layer · CSV specs
FAMILY E
National & sectoral evidence layer
Cross-border governance · Sectoral evidence
FAMILY F
Post-market monitoring, incident reporting, lifecycle & FRIA
Lifecycle module · PMM · Incident templates · FRIA (unified fundamental rights module)
FAMILY G
Governance, QMS & notified body selection
Notified body selection logic · Evidence · CSV
FAMILY H
Sector & country overlays
Employment · Healthcare/MedTech · Finance/AML · EU-27 country packs · EEA (3) · Combined sector × country templates
FAMILY 9 — EXTERNAL SUITE
GDPR & ePrivacy external template suite
Complete external-facing GDPR & ePrivacy documentation templates for controller and processor obligations
Aligned with
Binding regulatory framework
Conditional regulatory overlays
Standards & governance frameworks
Guidance & technical references
Decision Engine — Quick scope check
Does the EU AI Act
apply to your system?
The Decision Engine — Territorial Scope & Risk Classification — is always the first step. Answer three questions to see what the engine needs to determine, and what your next regulatory pathway looks like.
Pilot programme
Limited access.
Open now.
A selected number of organisations can access the full EACE engine at no cost, in exchange for a structured written review and formal assessment. Suitable for compliance teams, legal advisors, consultancies, audit firms, and AI governance practitioners evaluating the system before licensing.
Licensing & Enterprise
Structured pathways for every scale.
Access is provided through a controlled licensing model. Each path includes usage rights, access tiers, and a structured onboarding process designed to protect the system's integrity and ensure correct deployment.
Individual Licensing
For compliance professionals deploying EACE for their own systems or single-client engagements.
- Single-entity usage rights
- Full engine access
- Structured onboarding
- Version-controlled outputs
Partner Programme
For law firms and consulting practices using EACE as a back-end delivery system for client engagements.
- White-label delivery rights
- Multi-client deployment
- Priority access & support
- Co-branding options
Enterprise Onboarding
For organisations standardising AI governance across multiple systems, business units, or jurisdictions.
- Portfolio-wide deployment
- Custom sector overlays
- Dedicated onboarding
- SLA & audit support
02 · 03 · 04 — Standalone modules
Available separately.
All three modules are available independently of the core engine. Additional modules in development.
02 · Governance — Transparency (Light)
Transparency Notice Generator
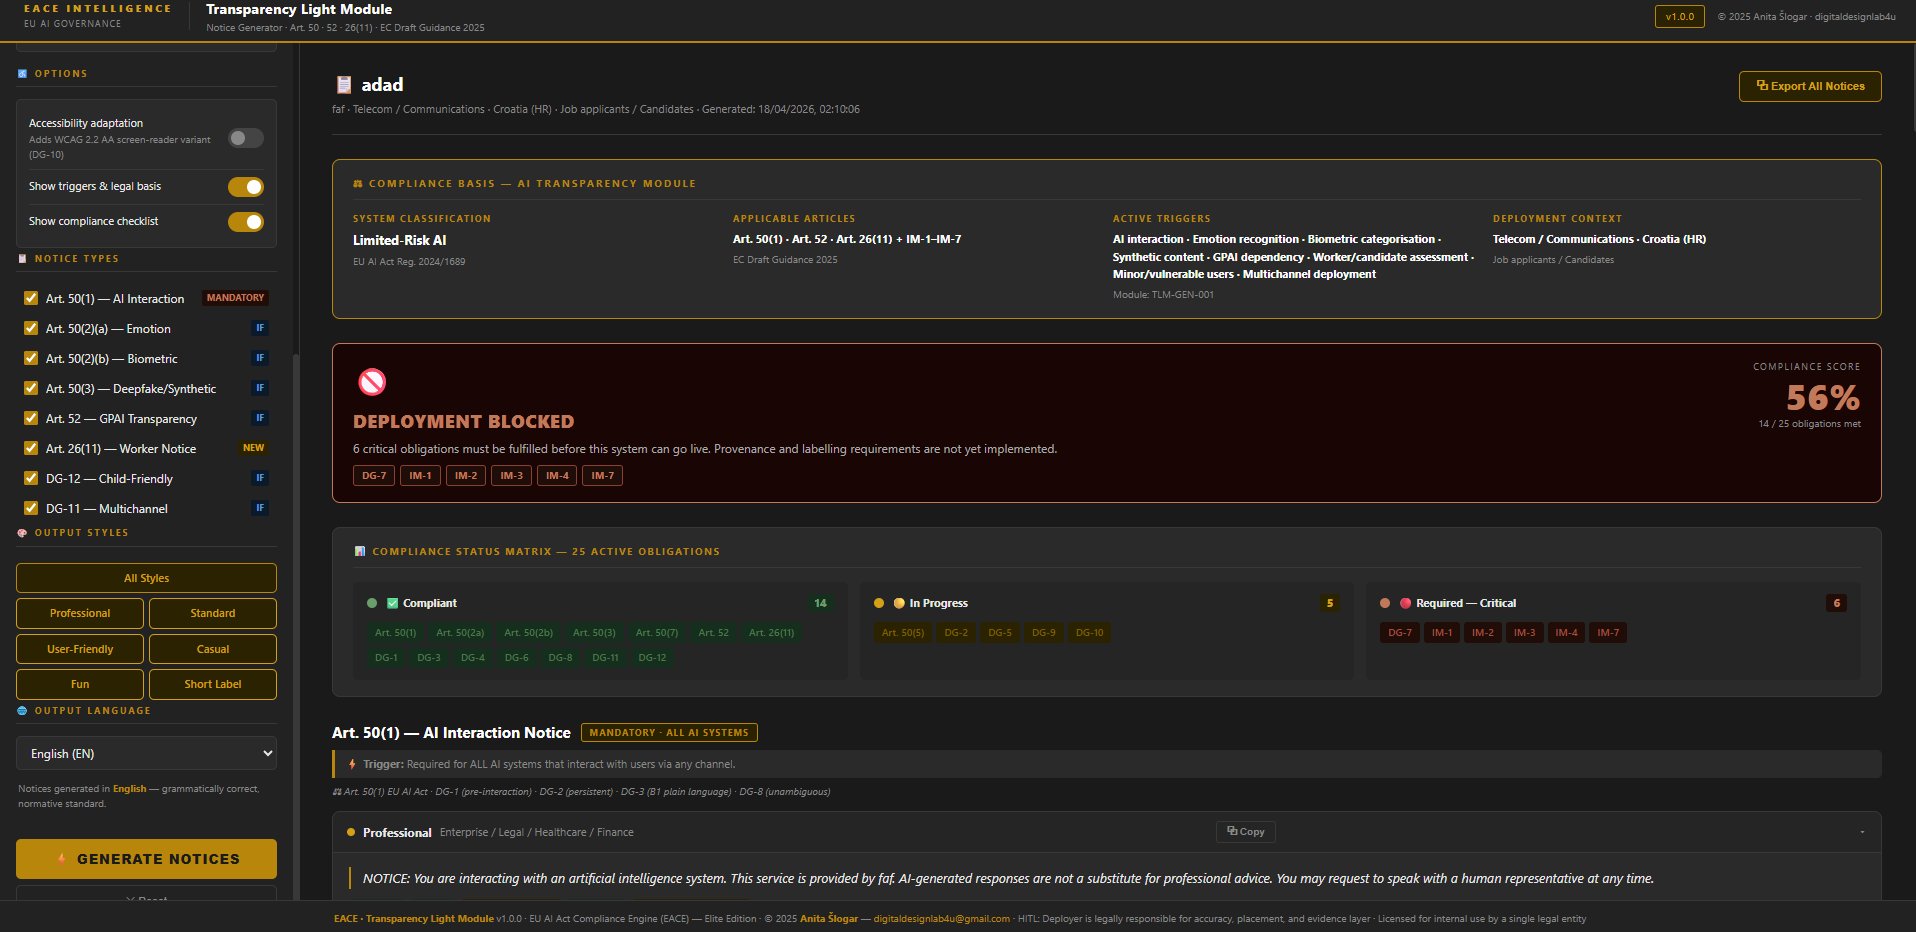
Generate EU AI Act-compliant transparency notices for any deployment context. Runs entirely in the browser — no backend, no API keys, no data transmission of any kind. 24 native output languages — every official EU language. EU+EEA deployments extend to 26. Seven deployment channels. Deployment gate with compliance scoring.
EU AI Act Art. 50, 26(11) · GDPR · ePrivacy · ISO/IEC 27001 · EC AI Office Guidance on Art. 50 (published 20 Jul 2026) · C2PA · IPTC · XMP
Learn more →03 · Risk & Governance
Risk & Governance Management System
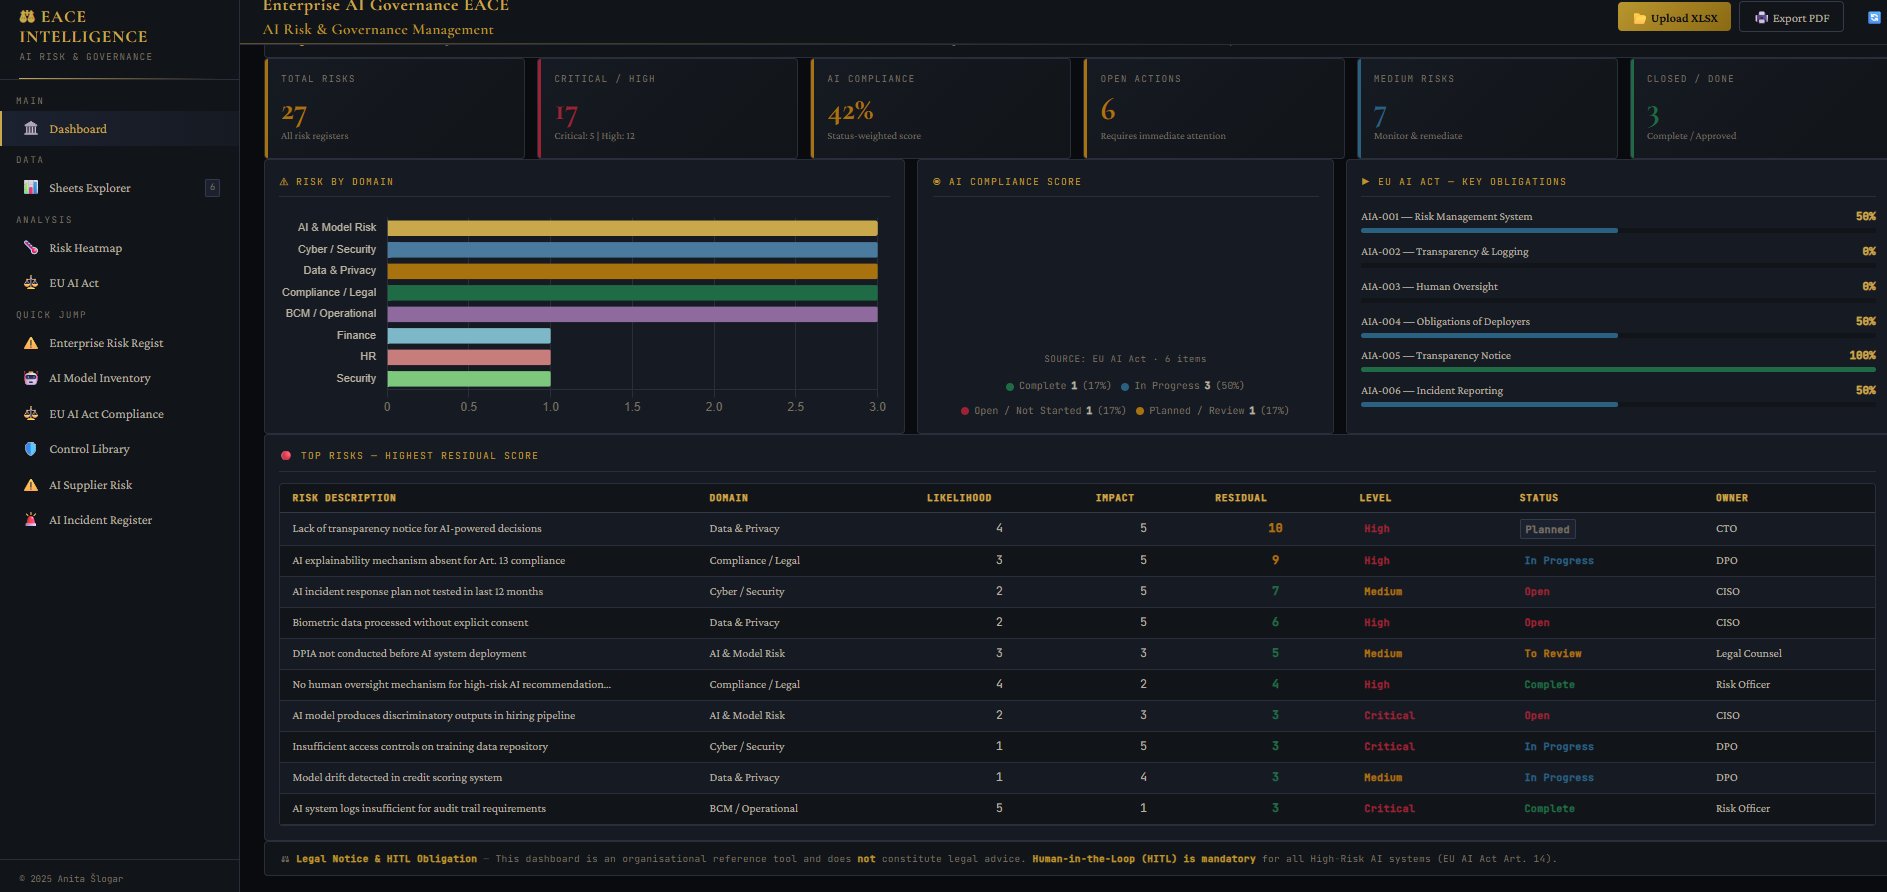
ISO 42001 AIMS-structured Excel engine — 30 sheets, a 20-control ISO-mapped Control Library. Lifecycle gates, risk-control mapping, FRIA/DPIA, HITL logging, supplier risk scoring. HTML offline dashboard. No SaaS dependency — for environments with strict data confidentiality requirements.
ISO/IEC 42001 · ISO/IEC 27001 · ISO/IEC 38505 · EU AI Act · GDPR · NIS2
Learn more →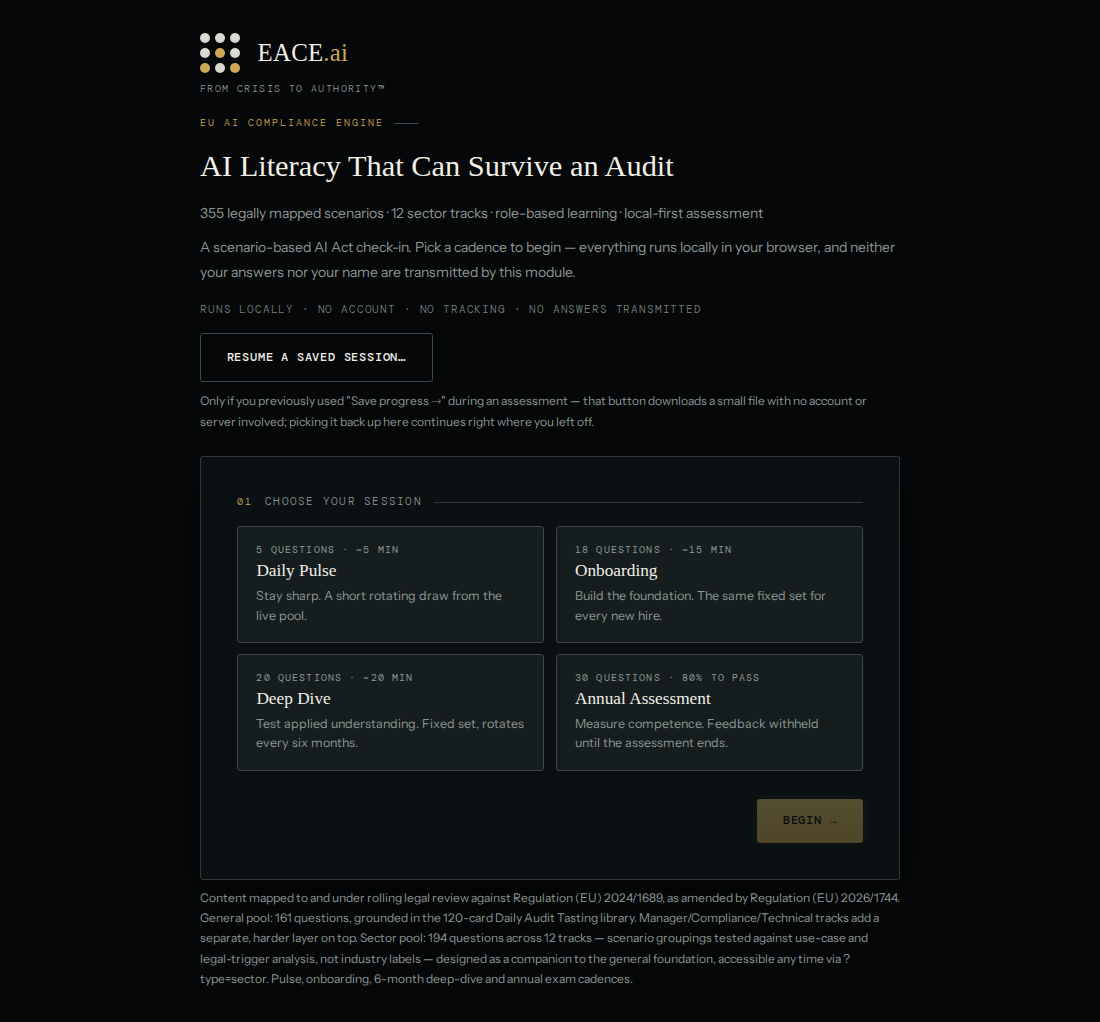
04 · Compliance Tasting Menu
EACE Compliance Tasting Menu
A standalone, scenario-based EU AI Act literacy assessment — 355 legally mapped questions across a general pool and 12 sector tracks, with dual-persona feedback from Alba and Kai on every answer. Four session cadences from a 5-question Daily Pulse to a formal Annual Assessment. Runs entirely in the browser — no account, no server, nothing transmitted. Optional signed Evidence Mode and a structured GRC Exchange export for your own governance tooling.
EU AI Act Art. 4 — AI literacy, as amended by Reg. (EU) 2026/1744 · content mapped across Arts. 2–99 & Annex III · GDPR
Learn more →Contact
Get in touch.
The EACE Engine and its modules are intellectual property available for licensing, white-label partnership, enterprise deployment, and strategic acquisition. We welcome enquiries from compliance professionals, consulting firms, and organisations preparing for EU AI Act obligations.